The Evolving Cybersecurity Ecosystem in India
Market Growth and Demand
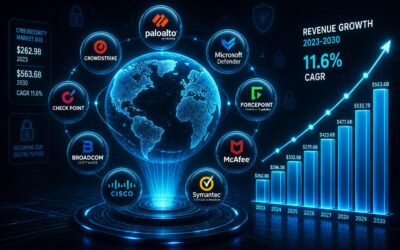
India’s cyber security market is experiencing a remarkable surge, projected to grow at a compound annual growth rate of over 15% in the coming years. This explosive growth is driven by the rapid digitization of financial services, healthcare, and government infrastructure. Businesses across the subcontinent are realizing that robust defense mechanisms are no longer an optional luxury, but a critical component of their operational continuity. The sheer volume of daily transactions and the explosion of connected devices have created a fertile ground for threat actors, compelling organizations to invest heavily in proactive security measures.
The demand for specialized expertise has never been higher, particularly for solutions that can preemptively identify vulnerabilities. Companies are shifting away from reactive protocols and moving towards predictive threat intelligence and zero-trust architectures. This shift has paved the way for both established global players and agile domestic startups to flourish. A few key drivers fueling this market expansion include:
– The mandatory implementation of data localization laws.
– The widespread adoption of cloud-based services among small and medium enterprises.
– A significant rise in state-sponsored cyber espionage activities.
– The integration of artificial intelligence in automated threat hunting.
As the threat landscape evolves with increasing sophistication, the search for the top 50 cyber security companies in india becomes a strategic necessity for enterprises seeking reliable partners. These organizations are not just providing tools; they are delivering comprehensive security frameworks that encompass endpoint protection, network security, and compliance management. With the government’s push towards a digitally empowered society, the opportunities for growth are immense, yet the margin for error remains razor thin.
Regulatory Landscape
India’s regulatory landscape now moves with unusual velocity. The Digital Personal Data Protection Act, 2023, imposes strict consent requirements, while CERT-In’s six hour incident reporting rule forces real-time vigilance. Companies no longer treat compliance as a checkbox; it is a continuous operational burden.
Enterprises evaluating the top 50 cyber security companies in india must weigh regulatory alignment heavily. The most capable vendors offer:
- automated breach detection tied to regulatory reporting feeds
- data residency assurance across hybrid cloud environments
- privacy impact assessments embedded in development pipelines
These functions directly address the pressures that regulators now place on business leaders. Without such capabilities, even technically advanced solutions fall short of what boards demand.
Key Industry Verticals
India’s financial sector processes over a billion UPI transactions every single day. Each one is a live attack surface, and the institutions responsible cannot afford a single moment of blindness. The top 50 cyber security companies in india largely built their reputations under these conditions.
Healthcare is the more uncomfortable story. Digitized patient records carry consequences that credit card numbers do not. A breach is not a financial inconvenience, it is a violation of bodily autonomy. I watch providers struggle to find vendors who grasp that distinction.
- Telecom networks underpin everything else, so their failure cascades quickly
- Manufacturing plants face operational technology threats that traditional IT defenses cannot touch
- Government infrastructure requires resilience under sustained state sponsored pressure
Each vertical demands a different kind of expertise, and that fragmentation defines India’s cybersecurity ecosystem.
Selection Criteria for Premier Cybersecurity Firms
Certifications and Compliance
Selecting from the top 50 cyber security companies in india demands more than reviewing client logos. We look at operational maturity. How quickly does a firm detect a simulated intrusion? Do their threat hunters monitor endpoints, cloud workloads, and legacy systems around the clock? The answers separate true defenders from resellers!
Certifications provide a hard baseline. ISO 27001 confirms a certified management system. SOC 2 Type II validates ongoing control over data security. However, we also need India-specific markers:
- Empanelled status with CERT-In or NCIIP
- ISO 27001 with current audit cycle
- SOC 2 Type II report without exceptions
- Valid vulnerability disclosure policy
Compliance alone cannot stop a determined attacker. Ask about mean time to response and how many threat hunts the team runs weekly. The right company will treat certification as a starting point, not a trophy.
Technology and Toolset
The technology stack of any candidate among the top 50 cyber security companies in india reveals more than marketing brochures. We look for platforms that unify endpoint detection, cloud workload protection, and identity monitoring in one console. Swivel-chair operations, where analysts manually move alerts between tools, are a red flag.
Strong firms automate triage and throttle low-fidelity alerts before they reach humans. They also feed active threat intelligence into detection rules within hours.
- Extended detection and response with full API access
- Threat hunting infrastructure that supports live payload detonation
- Attack surface management covering leaked credentials
Vendor demonstrations of incident response workflows reveal the difference. A firm relying on manual processes will struggle against today’s ransomware timelines. The right toolset means detection, containment, and forensic capture happen in minutes, not days.
Client Testimonials and Track Record
Client testimonials are the polite fiction of the industry, but track records are the ledger. When I assess the top 50 cyber security companies in india, I ask for references who will speak off the record. A firm that hesitates to connect you with a client who survived a ransomware attack has something to hide.
Look for patterns in their history. Did they detect breaches early or only after the damage spread? Have they retained the same security engineers for years? Turnover in this field often signals poor management.
- Request a list of clients who have been with them for over three years
- Ask about their response to a specific incident, not a generic one
- Check if their testimonials mention actual metrics like time to contain
The top 50 cyber security companies in india vary widely in quality. A solid track record includes failed engagements too, because honest firms learn from them. I trust those who admit when a deployment went sideways.
Pricing and Support Models
Selection criteria for premier firms go beyond billable hours. When evaluating the top 50 cyber security companies in india, look at how they price and support. Some charge flat retainers for continuous monitoring. Others use per endpoint pricing, which scales unpredictably as your network grows. Support models differ even more. The best firms name a dedicated engineer for your account. The rest route you through generic queues.
Ask about their after hours escalation. A genuine premier firm will commit to a 15 minute call back during an active incident. Many will not. Contract clauses for support response times should be explicit. The real test is pricing transparency. The top 50 cyber security companies in india include both those who hide fees in change orders and those who quote the full month upfront. Choose based on that.
Major Specializations in Indian Cybersecurity
Cloud and Application Security
Indian enterprises are shifting workloads to the cloud faster than security teams can adapt. That gap explains why the top 50 cyber security companies in india now pour serious resources into cloud and application security. These firms treat code as a vulnerability surface. They scan containers, APIs, and serverless functions before deployment, not after.
Specialization often splits into several disciplines:
- Cloud infrastructure posture management for AWS, Azure, and GCP
- Application security testing that combines static, dynamic, and interactive analysis
- Runtime protection for microservices and Kubernetes clusters
What separates the leaders is how they handle the software supply chain. They inspect third party libraries and open source dependencies with ruthless precision. They also watch for misconfigurations, which remain the leading cause of cloud breaches. For South African buyers evaluating vendors, depth in these two domains matters more than broad feature lists. The best Indian providers prove their skill through real incident response work, not marketing decks.
SOC and Managed Services
For many South African enterprises, the real value of the top 50 cyber security companies in india lies in their security operations centres. These SOCs run around the clock, correlating alerts from firewalls, endpoints, and identity systems. The emphasis is on active threat detection and response.
Managed services extend beyond basic triage. Providers build custom playbooks for each client’s environment, then test them through simulations. They also handle compliance reporting, which lightens the load for internal teams. Some firms offer dedicated threat hunters who probe for stealthy intrusion paths.
- Continuous log analysis and correlation
- Threat intelligence feeds tailored to financial and mining sectors
Indian SOC teams often outperform their global counterparts on cost and response speed. That combination makes them a practical choice for Capetonian or Johannesburg offices with limited security staff.
Risk and Compliance Consulting
Anyone who has wrestled with POPIA knows how quickly regulatory anxiety can spread. Indian risk and compliance consultancies respond with methodical precision. I have seen them translate dense legal text into actionable controls, aligning security strategies with business realities.
- Control gap assessments that benchmark specific operational units against industry frameworks.
- Audit simulation exercises that expose weaknesses before the official review.
- Continuous compliance monitoring that automates evidence collection and flagging deviations.
Rather than static reports, these firms build structured program management. They assign clear ownership, set measurable targets, and embed compliance tasks into existing software development cycles. That practical mindset saves Johannesburg teams hours of confusion during annual audits. It also explains why the top 50 cyber security companies in india attract international clients; their compliance advice often predicts regulatory shifts before local regulators publish them.
Incident Response and Forensics
Ransomware hit a Johannesburg logistics firm at 2 a.m. on a Sunday. The Indian incident response team was on a video call by 7 a.m., already imaging compromised servers and carving memory dumps for lateral movement traces. That speed matters. Forensic readiness separates the top 50 cyber security companies in india from the rest.
Indian forensic specialists treat every investigation like a crime scene. They preserve evidence with strict chain of custody, reconstruct timelines from system logs, and reverse engineer malware to find the entry point. Their reports hold up in court, which is critical for insurance claims and regulatory submissions in South Africa.
Common specializations include:
– Memory and disk forensics for ransomware attacks
– Cloud log analysis to trace unauthorized access
– Mobile device extraction for insider threat cases
These teams often discover the attack vector within hours, not weeks. They hand over a clear narrative of how the breach happened, what was taken, and what needs patching. That clarity keeps the top 50 cyber security companies in india as the first call for South African CISOs on incident day.
Future Directions and Innovation Hubs
AI and Machine Learning in Security
Machine learning has moved from product roadmaps to production across Indian cyber security firms. In Bengaluru and Hyderabad, innovation hubs train models on live attack telemetry. The top 50 cyber security companies in India now treat ML as core infrastructure.
Some vendors deploy unsupervised learning to map network anomalies before known signatures exist. Others use natural language processing on threat feeds in Hindi, Tamil, and English. This directly affects South African procurement. A vendor with serious ML capacity shrinks detection time from days to minutes.
Capabilities worth evaluating:
- Model retraining frequency and data freshness
- Access to proprietary incident datasets from Indian financial and manufacturing sectors
- Explainability features that show why an alert was generated
The advantage is applying research at scale. Indian firms convert academic papers into production tools, changing security pricing and delivery. When I speak with procurement teams in Johannesburg, this factor separates leading vendors from the rest.
Zero Trust Architecture Adoption
Pune and Bengaluru now function as living laboratories for the top 50 cyber security companies in india. These innovation hubs test architecture that assumes breach, not trust. The shift toward zero trust architecture adoption is deliberate. It changes how identity, device, and network segments interact. I see vendors moving from perimeter defense to continuous verification. The user experience remains smooth, but every request faces scrutiny.
Consider what this means for Johannesburg enterprises evaluating partners. The maturity of these hubs matters.
– Identity-driven micro-segmentation reduces lateral movement.
– Behavioral analytics create dynamic access policies.
– Integration with legacy infrastructure speeds deployment.
The top 50 cyber security companies in india are not waiting for international standards to dictate their pace. They build, test, and refine on local soil. This creates a procurement advantage for South African firms seeking proven, production-grade zero trust frameworks.
Cybersecurity Startups to Watch
India’s startup ecosystem for cyber security is moving into niche territory. Emerging companies in Hyderabad and Chennai are building firmware integrity checkers and deception platforms that misdirect attackers without costly hardware. These tools solve real problems for mid-sized enterprises.
What makes certain startups worth watching:
– Direct engagement with South African partners through co-development programmes
– Funding that supports deep research, not just marketing buzz
– Leadership teams with prior experience at major global security vendors
The top 50 cyber security companies in india already integrate these innovations through acquisition or partnership. For Johannesburg buyers, this means accessing frontier technology without the risk of importing unproven systems. Innovation hubs in India function as early warning radars for emerging threats, and their startup pipeline remains a practical resource for long-term security planning.
Government and Enterprise Initiatives
The concept of a cyber range, a controlled digital battlefield for simulating attacks, is moving from military applications to commercial necessity. Bengaluru and Pune now host facilities where incident response teams from the top 50 cyber security companies in india train against live threats. These environments replicate the complexity of a financial network under siege, offering a more visceral learning experience than any slideshow.
Government initiatives are shifting from policy documentation to operational funding. The proposed allocation for indigenous security research targets specific gaps in network forensics and hardware-level validation. I have seen enterprise adoption accelerate where public sector tenders require a certain percentage of locally developed technology, forcing global firms to partner with Indian innovators.
Key priorities driving this collaboration include:
– Establishing shared threat intelligence feeds between the public and private sectors.
– Funding university research on post-quantum cryptography.
– Creating sandboxed testing zones for critical infrastructure software.
This convergence of state backing and commercial agility ensures the top 50 cyber security companies in india remain at the vanguard of defensive strategy. For South African enterprises, the takeaway is clear. The pipeline of talent and technology emerging from these hubs is not theoretical. It is a practical resource for fortifying digital perimeters against increasingly sophisticated adversaries.

0 Comments